CrashPlan Platform is a unified data protection and cyber resilience solution designed to secure business-critical workloads across cloud, endpoint, and server environments. Built for scalability and security, the platform simplifies backup, recovery, and compliance management.
Why CrashPlan Platform?
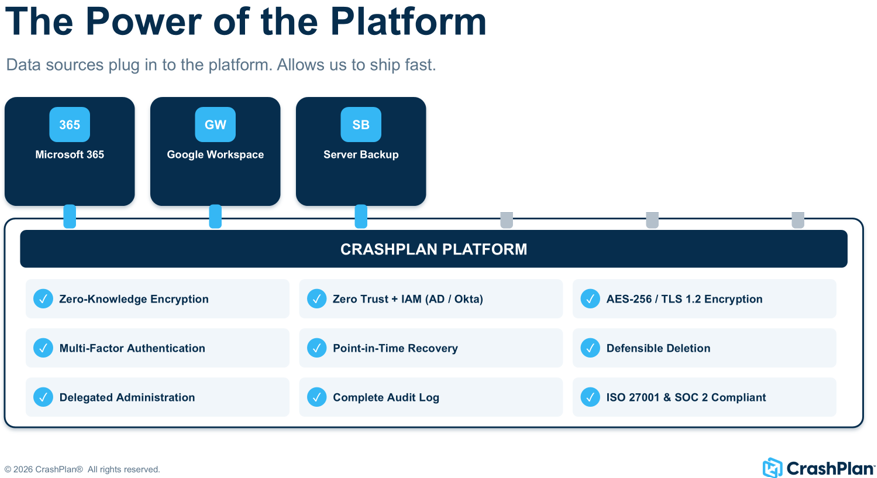
Unified protection for Microsoft 365, Google Workspace, and Server workloads
CrashPlan Platform delivers centralized backup and recovery across multiple business-critical workloads through a single management console. This unified approach eliminates the complexity of managing separate backup solutions for cloud collaboration suites and on-premises infrastructure. Administrators can enforce consistent policies, monitor backup health, and perform restores across all protected environments from one place.
Zero-Knowledge Encryption
CrashPlan uses a Zero-Knowledge Encryption model where encryption keys remain solely under customer control. Data is encrypted before it leaves the source and cannot be decrypted by CrashPlan or any third party. This architecture ensures complete data privacy and significantly reduces the risk of unauthorized access, making it ideal for organizations with strict confidentiality requirements.
Zero Trust + IAM integrations with Active Directory and Okta
The platform integrates with enterprise Identity and Access Management (IAM) systems such as Active Directory and Okta to enforce Zero Trust security principles. Authentication and authorization are continuously validated based on identity, role, and access context. This improves access control, simplifies user provisioning, and strengthens security across backup and restore operations.
AES-256 and TLS 1.2 Encryption
CrashPlan secures data both in transit and at rest using industry-standard encryption protocols. TLS 1.2 protects data during transmission between endpoints and the platform, while AES-256 encrypts stored backup data. This dual-layer protection ensures that sensitive information remains secure throughout its lifecycle and aligns with enterprise security best practices.
Point-in-Time Recovery
Point-in-Time Recovery enables administrators and users to restore data from specific backup versions captured at precise moments.
This allows recovery from accidental deletions, ransomware attacks, data corruption, or unwanted changes. By restoring exactly what is needed from a known-good point, organizations can reduce downtime and improve business continuity.
Defensible Deletion for Secure Data Lifecycle Management
Defensible Deletion ensures that data is removed in a controlled, auditable, and policy-driven manner. This helps organizations meet regulatory requirements for data retention and disposal while reducing unnecessary storage consumption. It also minimizes legal and compliance risks by ensuring expired or obsolete data is securely purged.
Complete Audit Logs for Compliance and Governance
Every critical platform activity—including backups, restores, policy changes, user actions, and administrative events—is recorded in detailed audit logs. These logs provide full operational transparency and support internal reviews, security investigations, and compliance audits. Organizations can demonstrate accountability and maintain governance over their data protection environment.
ISO 27001 and SOC 2 Compliant Architecture
CrashPlan Platform is built on a security-first framework aligned with globally recognized compliance standards such as ISO 27001 and SOC 2. These certifications validate the platform’s controls for data security, availability, confidentiality, and operational integrity. This gives customers confidence that their backup environment meets stringent enterprise and regulatory requirements.